Search
Table of contents
- What Is Quantum Security? Preparing for the Post-Quantum Era
-
What Is a Cryptography Bill of Materials (CBOM)?
- Why Is a CBOM Important?
- Benefits of a CBOM
- How Does a CBOM Work?
- Example: Using a CBOM to Identify Cryptographic Risk
- How Does a CBOM Support Post-Quantum Cryptography Migration?
- Best Practices for CBOM Management
- Threat Intelligence: How Cryptographic Threats Affect CBOM Priorities
- How to Implement a CBOM
- Challenges of CBOM Management
- Future Trends in CBOM Management
- CBOM FAQs
- Quantum Readiness: How to Prepare for Post-Quantum Security
-
What Is Q-Day? Quantum Computing and Cyber Risk
- Why Experts Disagree About When Q-Day Will Happen
- What Would Happen If Q-Day Arrived Tomorrow?
- Why Harvest-Now, Decrypt-Later Matters More Than Q-Day Itself
- Unit 42 Perspective: Q-Day Risk Starts With Today’s Data Theft
- How Close Are We to Q-Day?
- What Are Governments and Standards Bodies Doing to Prepare?
- How to Prepare for Q-Day Without Overreacting
- Will Q-Day Be a Crisis or a Milestone?
- Q-Day FAQs
- NIST PQC Migration Strategies: Steps, Standards & Tips
-
What Is Post-Quantum Cryptography (PQC)? A Complete Guide
- Post-Quantum Cryptography Explained
- The Quantum Threat to Modern Encryption
- How Post-Quantum Cryptography Works
- Standardized Algorithms: NIST FIPS 203, 204, and 205
- Preparing for the Post-Quantum Transition
- PQC Challenges and Implementation Pitfalls
- How Can Organizations Prepare for PQC?
- Post-Quantum Cryptography FAQs
-
What Are NIST PQC Standards?
- NIST PQC Standards Explained
- The Urgency of Quantum-Resistant Cryptography
- What Is the Timeline for PQC Adoption?
- Core NIST PQC Standards and Finalized Algorithms
- What PQC Standards Exist Today?
- How Do Global PQC Standards and Policies Differ?
- What Is Hybrid Cryptography?
- How NIST PQC Standards Differ from Classical Encryption
- Strategic Migration: Implementing NIST PQC Standards
- Unit 42 Insights: The Evolving Threat Landscape
- Overcoming PQC Implementation Challenges
- PQC Readiness: What to Do Now
- Quantum security FAQs
-
8 Quantum Computing Cybersecurity Risks + How to Prepare
- What Are Quantum Computing Cybersecurity Risks?
- Why Quantum Computing Threatens Cybersecurity
- 1. Breaking Public-Key Encryption
- 2. Harvest-Now, Decrypt-Later Attacks
- 3. Forgery of Digital Signatures
- 4. Compromise of Secure Boot Processes
- 5. Vulnerability of Financial Transactions and Ledgers
- 6. Decryption of Historical Data Backups
- 7. Identity and Access Management Failure
- 8. Obsolescence of Legacy IoT and Embedded Systems
- Quantum Threat and Readiness Timeline
- How Organizations Can Prepare For Quantum Cybersecurity Risks
- Quantum Computing Cybersecurity Risk Examples
- What changed recently in post-quantum cybersecurity?
- Quantum Computing Cybersecurity Risks FAQs
What Is Harvest Now, Decrypt Later (HNDL)?
5 min. read
Table of contents
Harvest now, decrypt later is a cyberattack strategy in which adversaries collect encrypted data today and store it until future quantum computers can decrypt it. Also known as store now, decrypt later, HNDL creates immediate risk for sensitive data that must remain confidential for years or decades.
The threat matters now because the data being stolen today may still be valuable when quantum decryption becomes practical. Organizations cannot wait for Q-Day to begin preparing. They need cryptographic visibility, data prioritization, crypto-agility, and post-quantum migration planning before quantum-capable attacks become operationally viable.
Key Points
-
Harvest now, decrypt later is a present-day risk: Attackers can collect encrypted data now and wait for future quantum computers to decrypt it. -
Long-lived sensitive data is most exposed: Government records, financial data, healthcare information, intellectual property, and defense data may remain valuable for decades. -
Public-key cryptography creates the biggest concern: RSA and elliptic-curve cryptography are expected to be vulnerable to sufficiently powerful quantum computers. -
Q-Day does not need to arrive for the risk to begin: The risk starts when encrypted data is intercepted, copied, or stolen. -
Post-quantum migration should begin now: Organizations need cryptographic inventories, crypto-agility, vendor readiness, and migration roadmaps to reduce future exposure.
How Does a Harvest Now, Decrypt Later Attack Work?
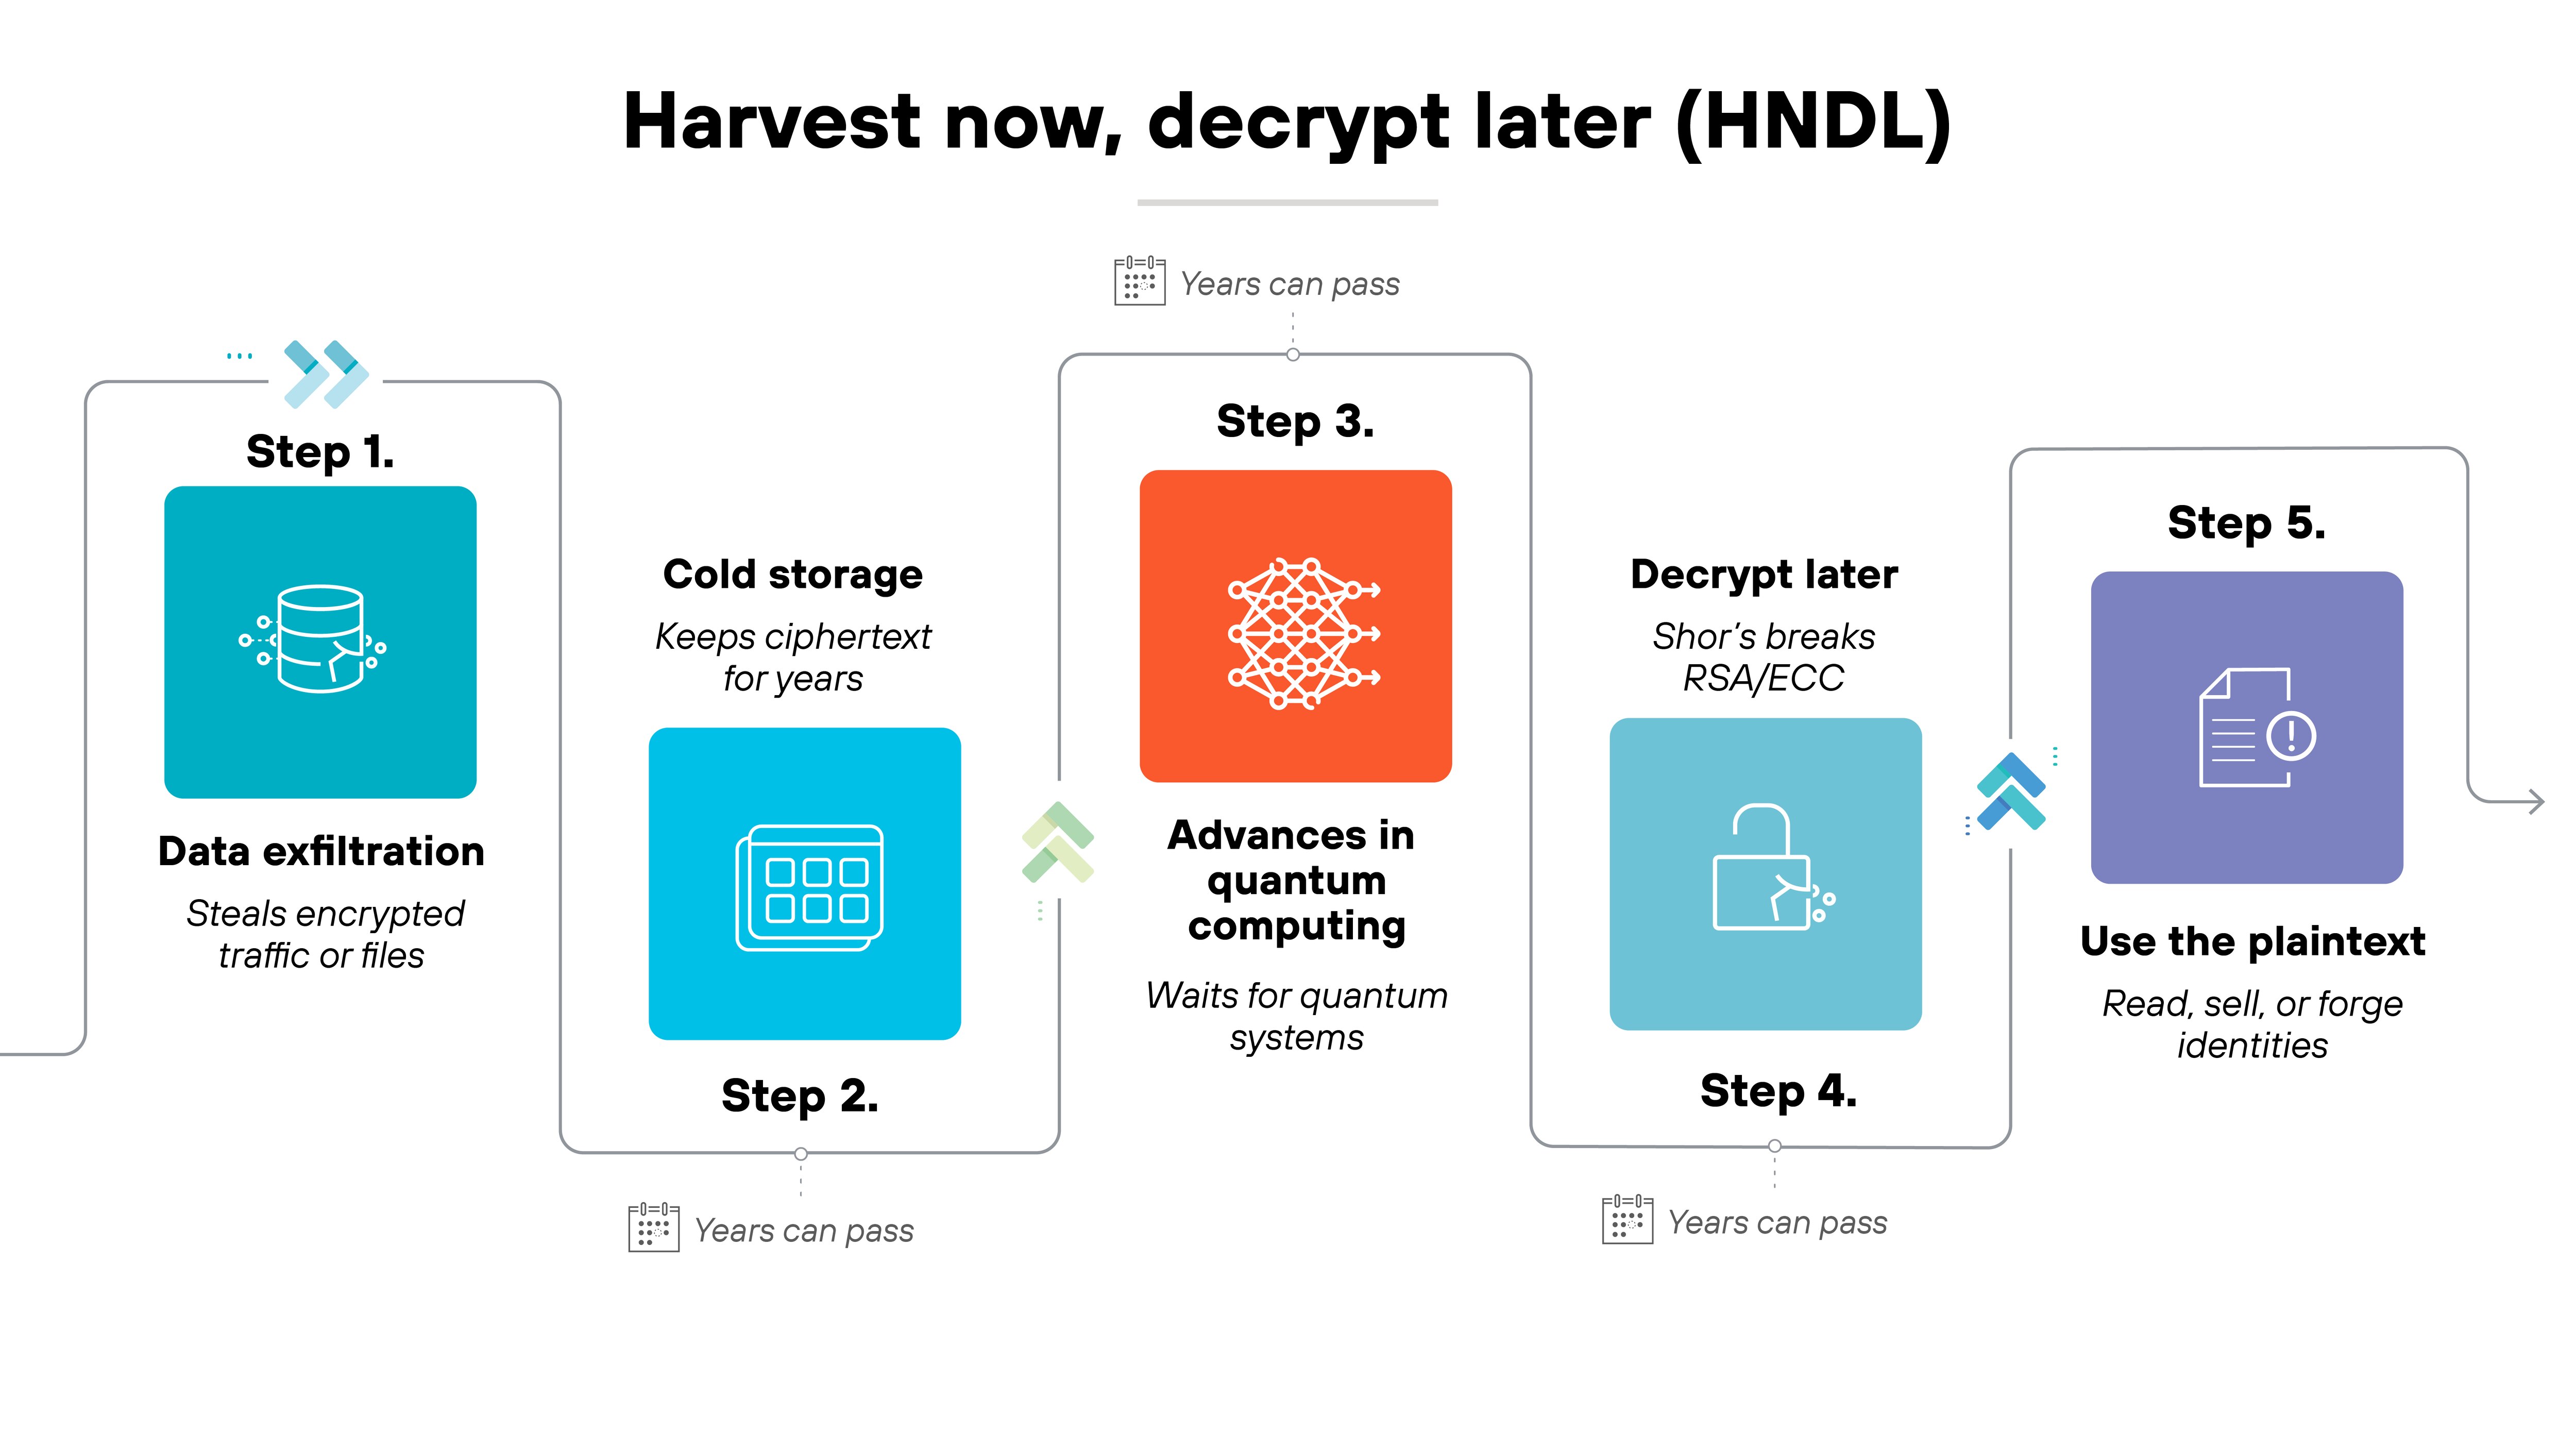
A harvest now, decrypt later attack happens in three stages:
- Phase 1: Data collection
- Phase 2: Long-term storage
- Phase 3: Future decryption
The attack does not require adversaries to break encryption immediately. Instead, they steal or intercept encrypted data, preserve it, and wait until quantum computing can make decryption feasible.
This delayed attack model is what makes HNDL difficult to detect and hard to reverse. Once encrypted data has been collected, organizations cannot “unharvest” it.
Phase 1: Harvest
Attackers collect encrypted information through methods that already exist today. This may include intercepting network traffic, compromising endpoints, exploiting servers, accessing cloud storage, or collecting data from exposed systems.
The data may still be unreadable at the time of theft. That does not make it safe. For an attacker, encrypted data can become a future asset if it has long-term value.
Phase 2: Store
After collection, attackers archive the encrypted data for future use.
This phase may last years or decades. The data may sit in private repositories, criminal infrastructure, state-backed archives, or long-term intelligence stores until quantum decryption becomes possible.
This is why HNDL is so dangerous: the storage phase is passive. There may be no ongoing activity for defenders to detect.
Phase 3: Decrypt
When cryptographically relevant quantum computers become capable of breaking vulnerable public-key algorithms, adversaries may be able to decrypt stored data.
A sufficiently powerful quantum computer could use algorithms such as Shor’s algorithm to threaten RSA and elliptic-curve cryptography. At that point, data that was previously protected by classical public-key encryption could become readable.
The result is not a new breach. It is the delayed impact of data stolen earlier.
Unit 42 Perspective: Data Theft Is Already Moving Faster
Unit 42 insight: Attackers do not need quantum computers to create quantum-era risk. They only need access to encrypted data that will still be valuable when quantum decryption becomes practical.
Unit 42 research shows why harvest-now, decrypt-later risk cannot be treated as a future-only problem. In the 2026 Unit 42 Global Incident Response Report, the fastest quartile of intrusions reached data exfiltration in 72 minutes in 2025, compared with 285 minutes in 2024. The share of incidents reaching exfiltration in under one hour also increased from 19% in 2024 to 22% in 2025.
This acceleration matters for quantum security because HNDL begins at the moment encrypted data is collected, not when quantum computers become capable of decrypting it. Once sensitive encrypted data is stolen, organizations may not be able to reduce its future exposure retroactively.
Unit 42 has also observed attackers exfiltrating data earlier in the attack process and rapidly collecting large volumes of information before sorting through it later. That behavior aligns with the HNDL risk model: collect now, preserve value, and exploit later.
Why HNDL Matters Before Quantum Computers Exist
"Encrypted data remains at risk because of the 'harvest now, decrypt later' threat in which adversaries collect encrypted data now with the goal of decrypting it once quantum technology matures. Since sensitive data often retains its value for many years, starting the transition to post-quantum cryptography now is critical to preventing these future breaches. This threat model is one of the main reasons why the transition to post-quantum cryptography is urgent."
- NIST, Transition to Post-Quantum Cryptography Standards
The HNDL threat matters because data and encryption have different lifespans.
Sensitive data may need to remain confidential for 10, 20, or 30 years. But the cryptography protecting that data may not remain strong for the same length of time. If encrypted data is collected today and the algorithm protecting it becomes breakable later, the data becomes exposed.
That mismatch is the core of HNDL risk.
Examples of long-lived data include:
- Government and diplomatic records
- Defense and intelligence information
- Financial records
- Medical records and genetic data
- Legal documents
- Intellectual property
- Product designs
- Research data
- Long-term identity records
Organizations should not measure risk only by whether quantum computers can break encryption today. They should measure risk by how long the data must remain protected.
If the data’s confidentiality lifespan extends beyond the expected strength of the cryptography protecting it, the organization has quantum-era exposure.
Further reading: 8 Quantum Computing Cybersecurity Risks [+ Protection Tips]
Which Organizations and Data Are Most Exposed?
Organizations with long data retention requirements and high-value confidential information face the greatest harvest-now, decrypt-later exposure.
| Sector | Data Most at Risk | Why It Matters |
|---|---|---|
| Government | Diplomatic communications, census data, classified archives | Diplomatic communications, census data, classified archives |
| Defense and aerospace | R&D, supply chain data, schematics, operational intelligence | Long-term strategic value makes stored data attractive to nation-state actors. |
| Financial services | Transaction records, customer PII, contracts, payment data | Financial data can support fraud, intelligence gathering, and regulatory exposure. |
| Healthcare and life sciences | Medical records, genetic data, clinical research | Health data has a long confidentiality lifespan and high personal impact. |
| Cloud and service providers | Customer data stores, encrypted traffic, cross-border transfers | Providers often process or store sensitive data across many sectors. |
| Critical infrastructure | Operational data, system designs, vendor dependencies | Exposure could affect national resilience and future operational security. |
The risk increases in distributed environments. Multi-cloud architecture, global data sharing, remote access, SaaS adoption, and third-party integrations create more places where encrypted traffic or stored data can be intercepted, copied, or retained.
How Attackers Exploit the Window Before PQC
Attackers do not need to wait for quantum computers to act. They can collect encrypted data now while organizations are still using classical cryptography.
State-backed groups, advanced persistent threat actors, and well-resourced criminal groups may view encrypted data as a long-term investment. Even if the data cannot be read today, it may become valuable later.
Some encrypted data may also be useful before decryption. Metadata can reveal relationships, communication patterns, business priorities, infrastructure dependencies, and operational behavior.
This makes HNDL a low-risk, high-reward strategy for adversaries. They can collect now, store quietly, and wait for technology to catch up.
How HNDL Connects to Q-Day
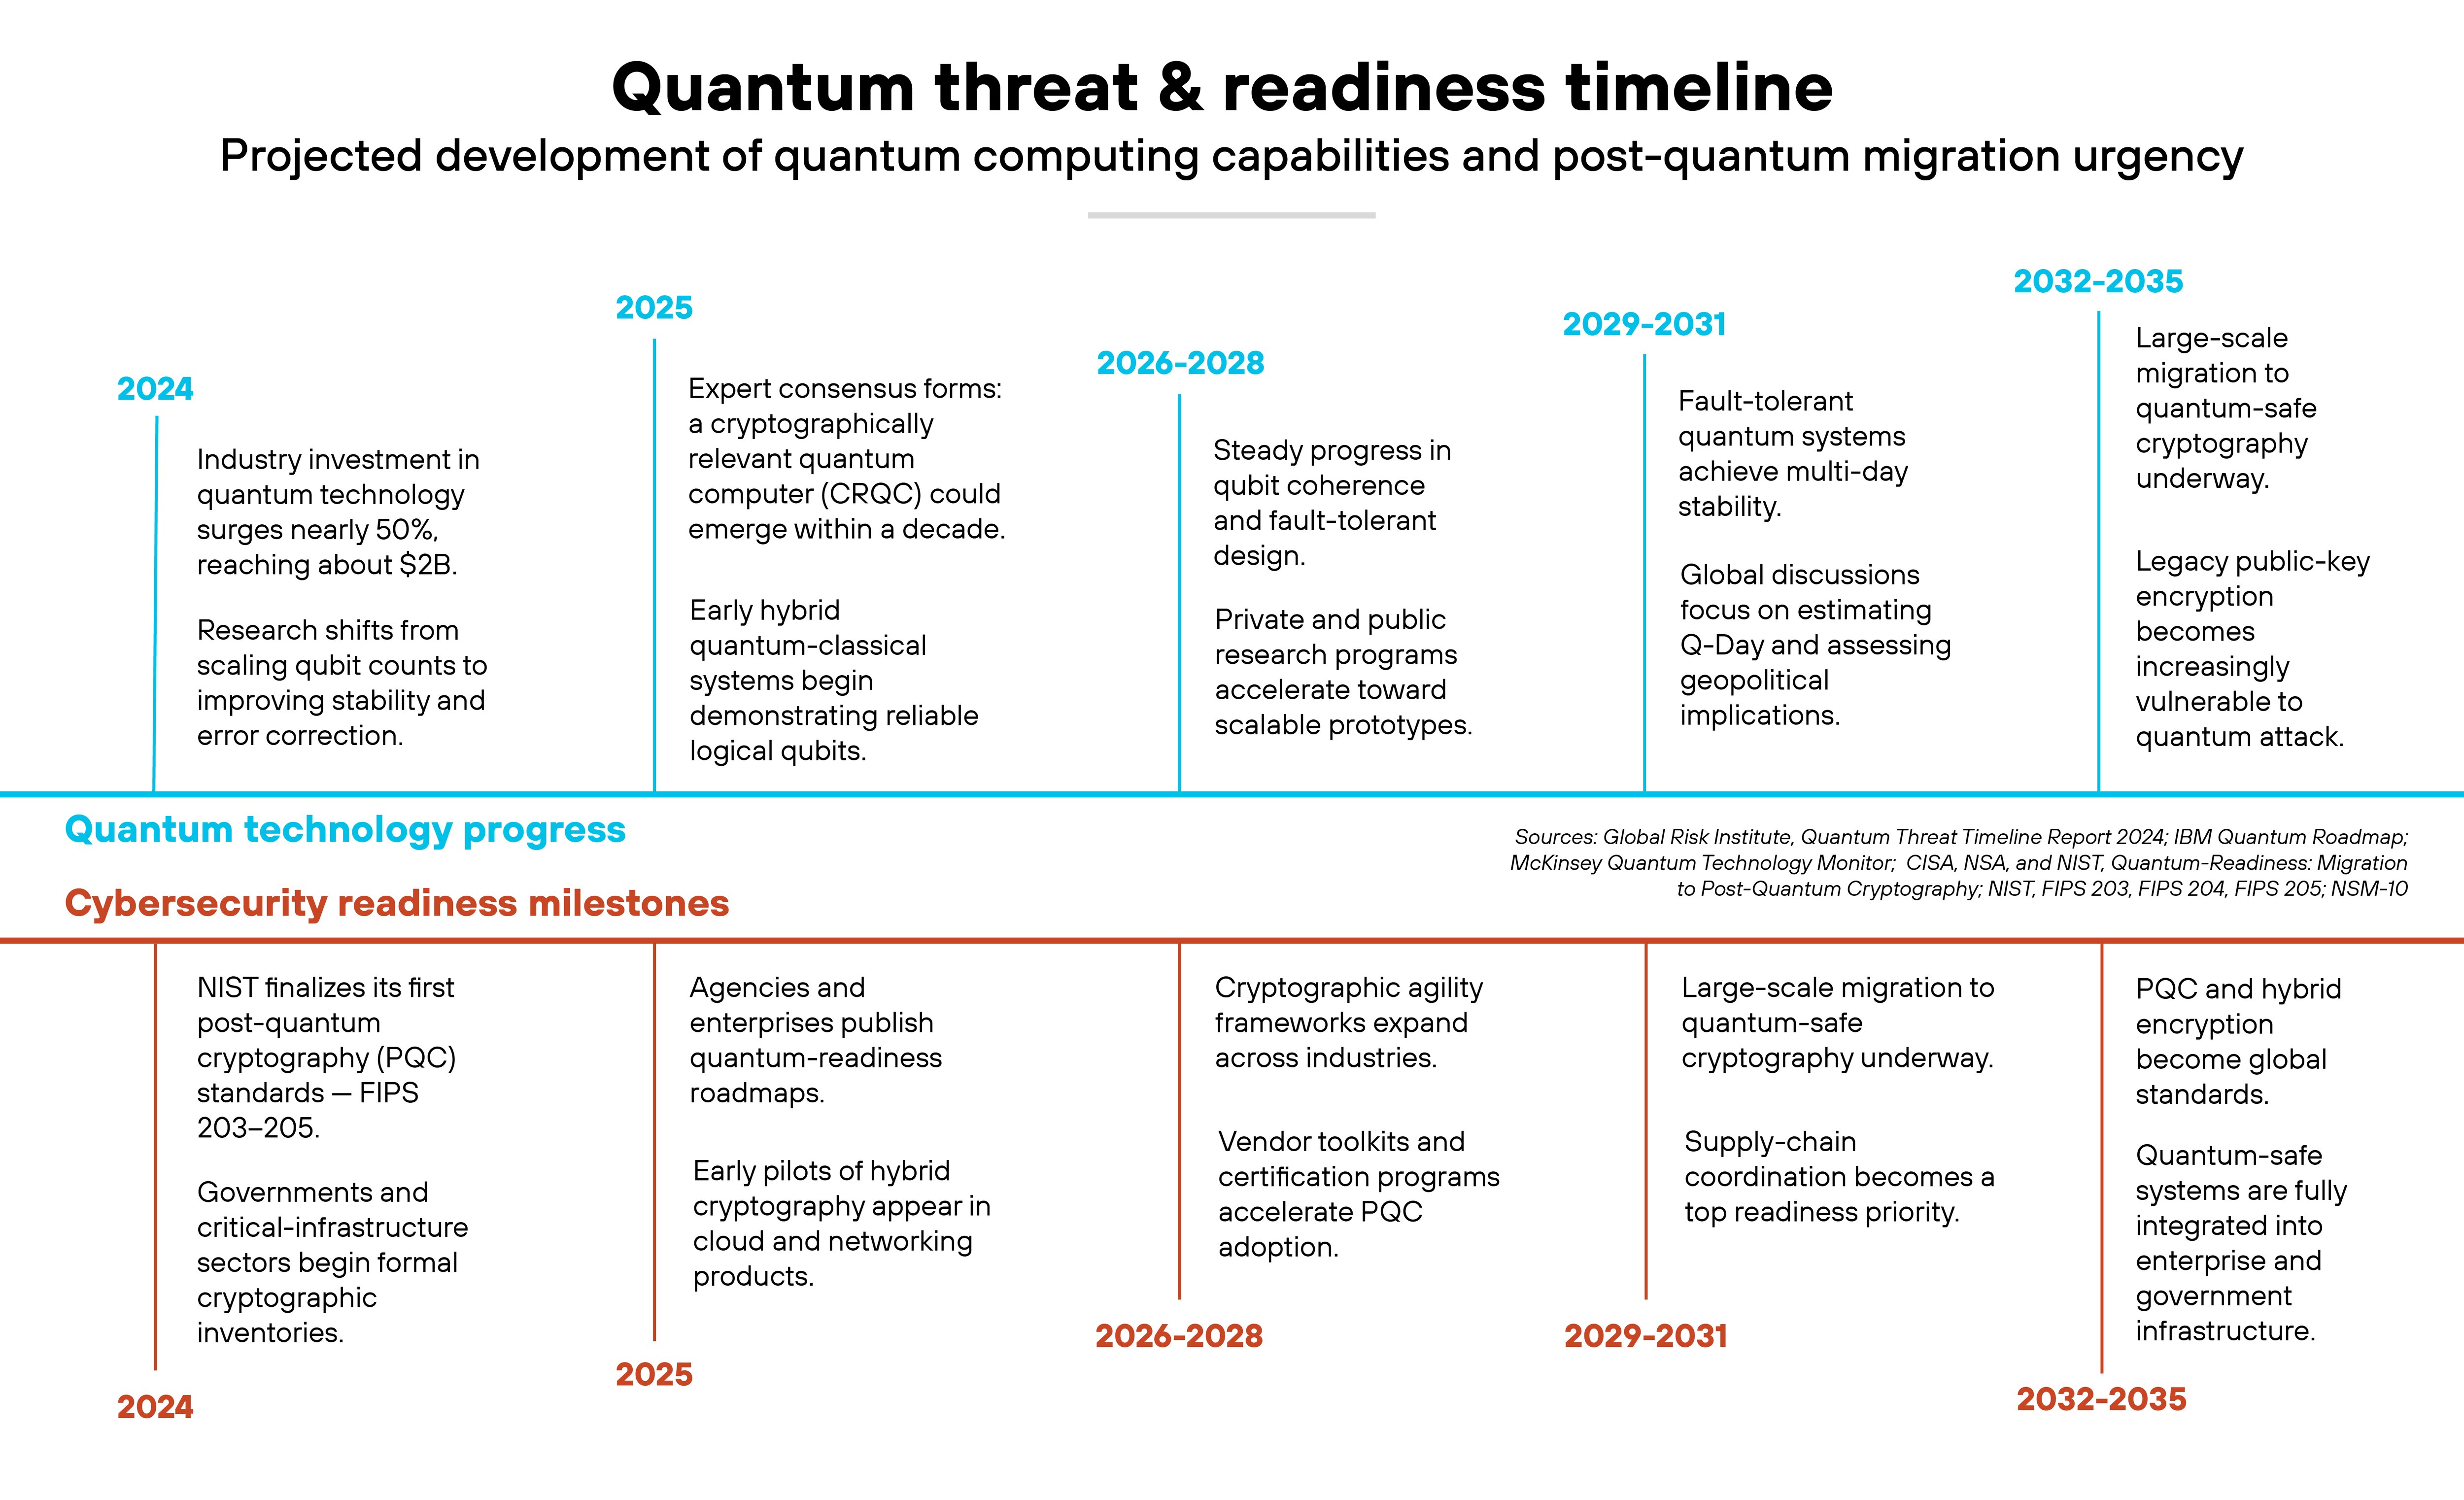
Q-Day is the point when quantum computers become powerful enough to break widely used public-key cryptography, such as RSA and elliptic-curve cryptography.
No one knows the exact date Q-Day will occur. Most expert projections place cryptographically relevant quantum computers in the 2030s or later, but timelines vary because quantum hardware, error correction, scalability, and algorithmic progress remain uncertain.
For HNDL, the exact date matters less than the preparation window.
If attackers collect encrypted data today, organizations cannot protect that stolen data retroactively once Q-Day arrives. That means preparation must begin before quantum decryption becomes practical.
The goal is not to predict Q-Day perfectly. The goal is to reduce what adversaries can harvest before Q-Day happens.
How to Prepare for Harvest-Now, Decrypt-Later Attacks
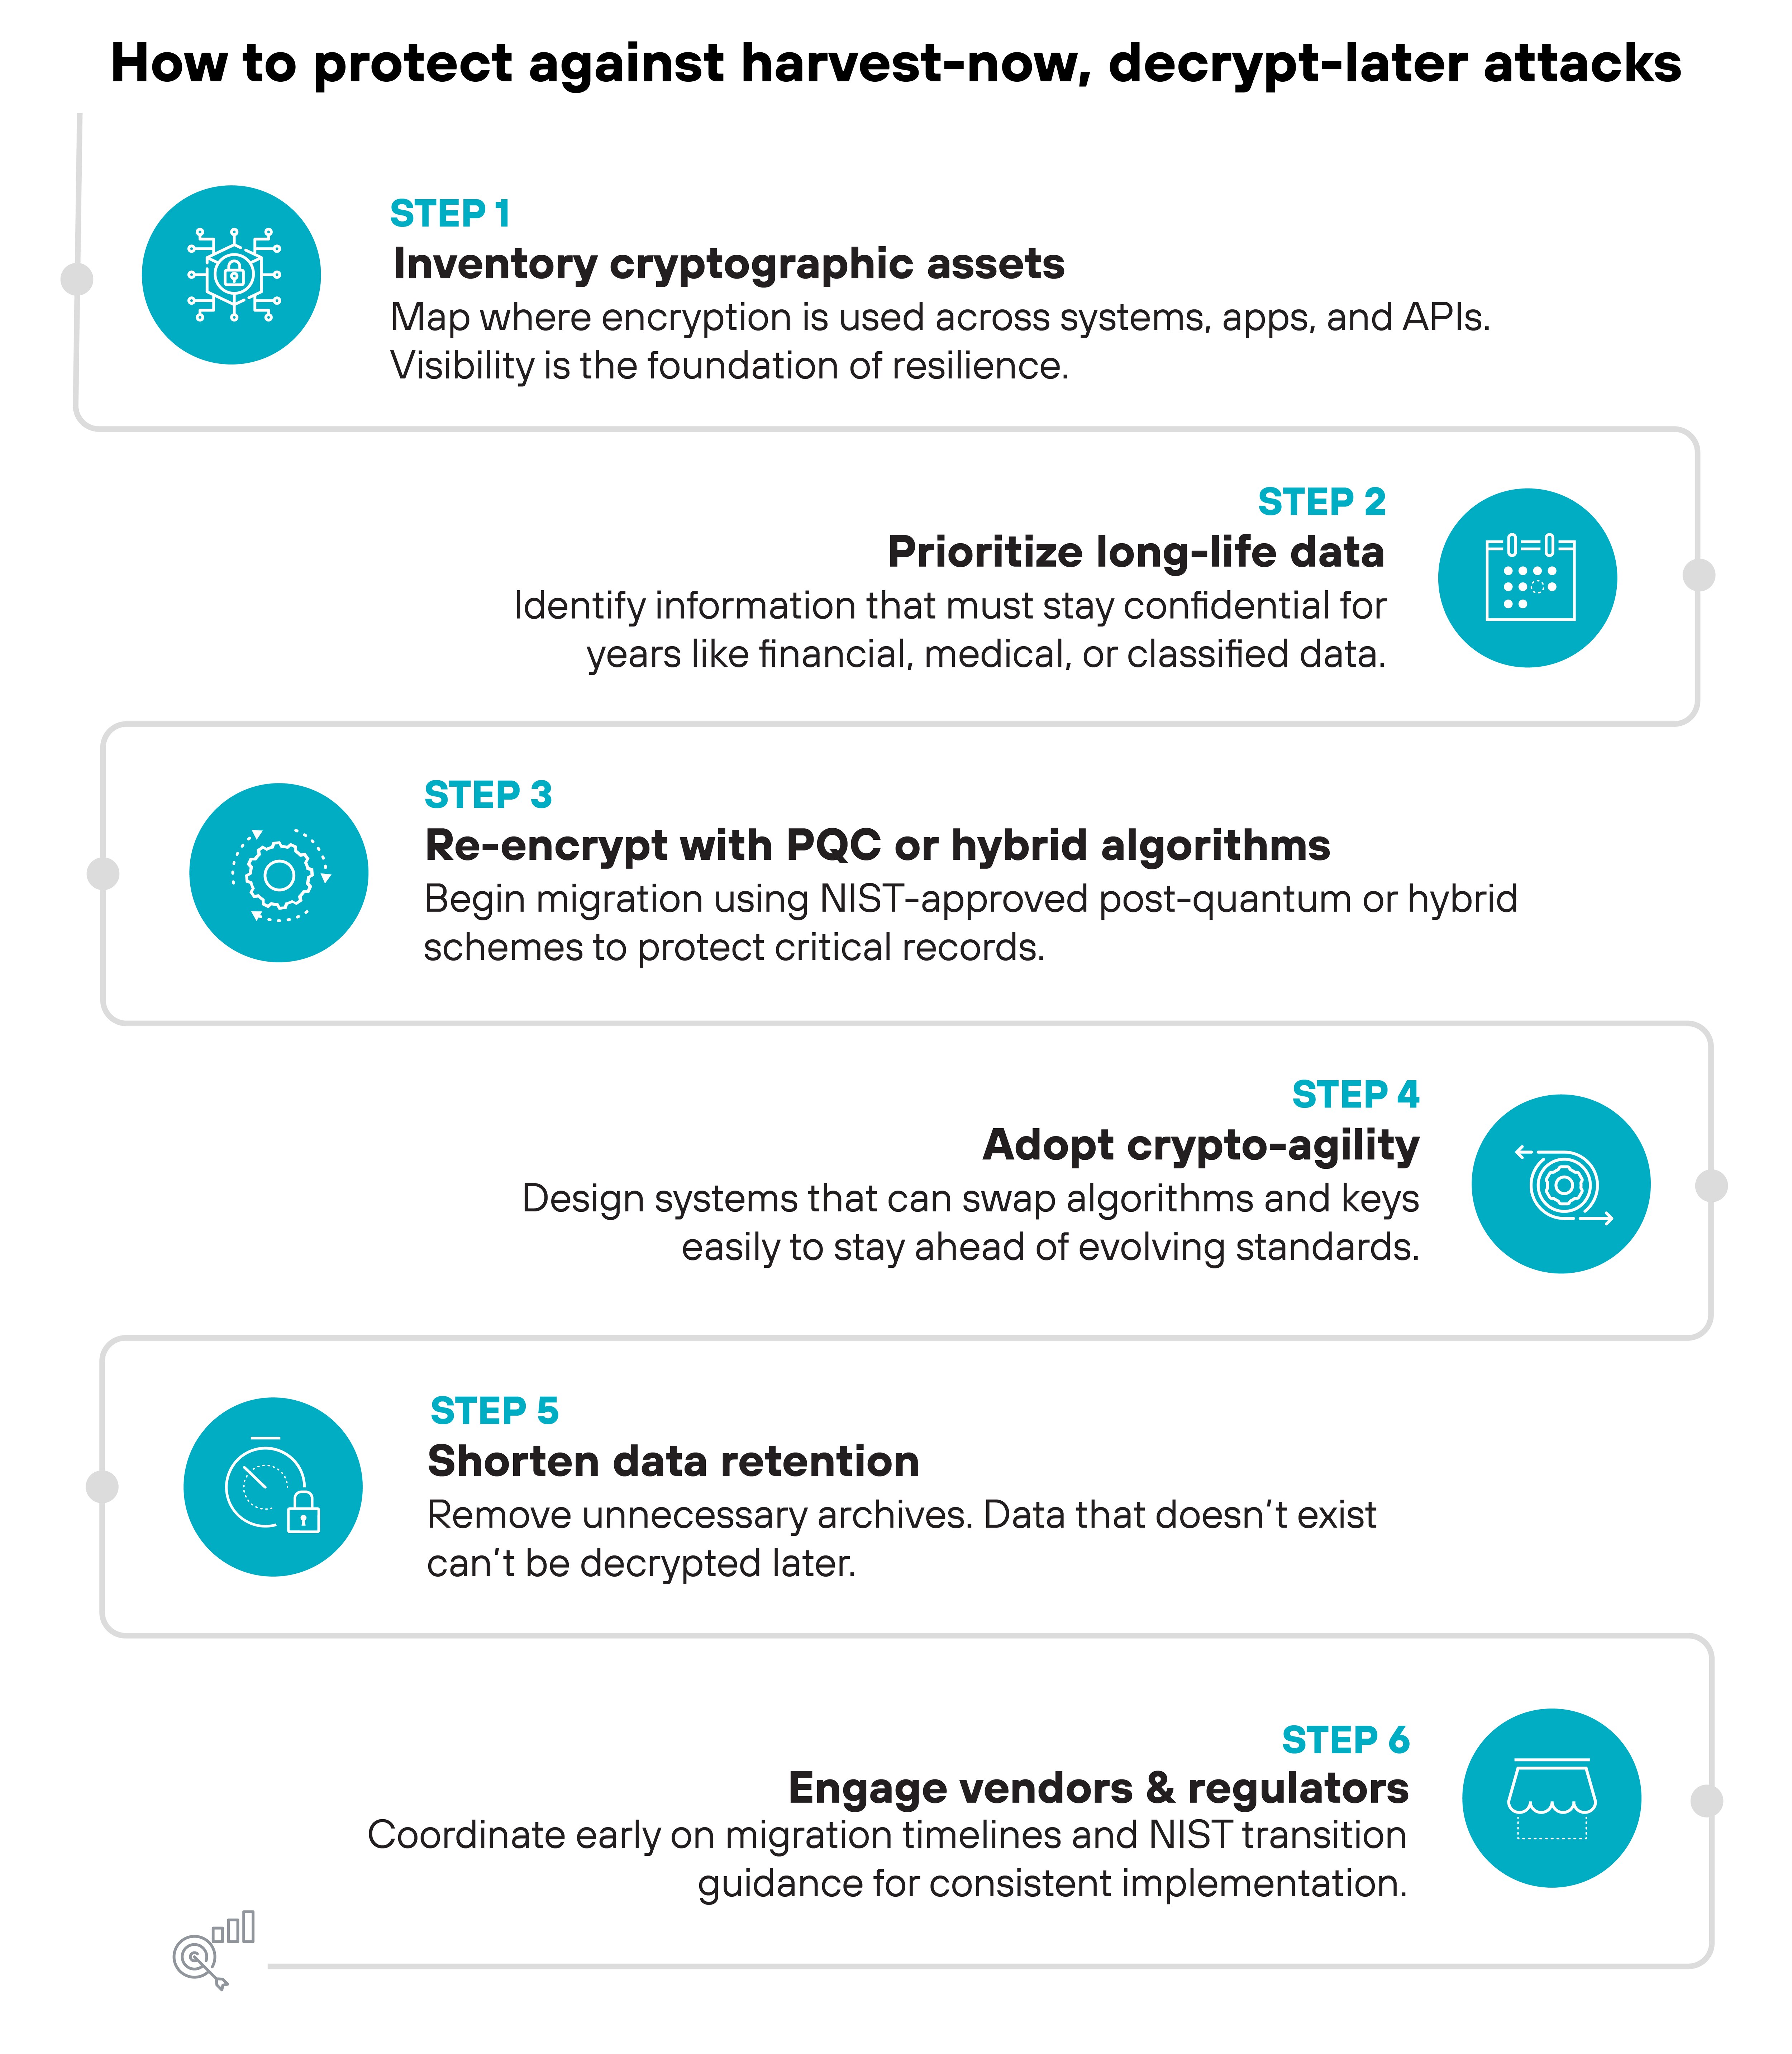
Defending against HNDL requires a practical post-quantum readiness strategy. Organizations should focus first on visibility, prioritization, and cryptographic agility.
1. Inventory Cryptographic Assets
Identify where encryption, keys, certificates, cryptographic libraries, algorithms, and protocols are used across the environment.
A cryptographic inventory should cover:
- Applications
- APIs
- Databases
- Certificates
- PKI systems
- Cloud services
- Network devices
- IoT and OT systems
- Third-party platforms
- Vendor-managed services
This inventory gives teams the baseline needed to assess exposure and prioritize migration.
2. Prioritize Long-Lived Sensitive Data
Not all data carries the same HNDL risk.
Focus first on data that must remain confidential for years or decades. This includes regulated records, intellectual property, government information, classified data, healthcare data, and long-term identity information.
If the data will still matter when quantum decryption becomes feasible, it should be treated as high priority.
3. Adopt Post-Quantum or Hybrid Cryptography
Begin testing post-quantum cryptography and hybrid models where appropriate.
NIST finalized its first post-quantum cryptography standards in 2024, including FIPS 203 for ML-KEM, FIPS 204 for ML-DSA, and FIPS 205 for SLH-DSA. These standards provide a foundation for quantum-resistant key encapsulation and digital signatures.
Hybrid cryptography can help organizations combine classical and post-quantum approaches during transition periods. This can reduce migration risk while standards, products, and interoperability mature.
4. Build Crypto-Agility
Crypto-agility is the ability to replace cryptographic algorithms, keys, certificates, and protocols without redesigning entire systems.
For HNDL defense, crypto-agility helps organizations respond as standards evolve, vulnerabilities are discovered, or migration requirements change.
Crypto-agility should apply to:
- Algorithm replacement
- Key rotation
- Certificate lifecycle management
- Protocol updates
- Vendor integrations
- Application development practices
5. Reduce Data Retention
Data that no longer exists cannot be decrypted later.
Organizations should review retention policies and delete data that is no longer needed for business, legal, or compliance purposes. Reducing unnecessary archives lowers the volume of sensitive data that attackers can harvest.
This is especially important for old backups, unmanaged data stores, legacy archives, and duplicated records.
6. Engage Vendors and Partners
Many cryptographic dependencies sit outside internal systems.
Organizations should ask vendors whether their products support post-quantum cryptography, crypto-agility, certificate updates, key rotation, and NIST-aligned migration roadmaps.
Vendor readiness should become part of procurement, renewal, and security review processes.
7. Create a Quantum Readiness Roadmap
A quantum readiness roadmap should define ownership, milestones, dependencies, high-risk systems, vendor requirements, and migration timelines.
The roadmap should answer:
- Which data is most exposed to HNDL?
- Where is quantum-vulnerable cryptography used?
- Which systems should migrate first?
- Which vendors are dependencies?
- What must be tested before deployment?
- How will progress be measured?
The objective is to make post-quantum migration planned, governed, and measurable.
How HNDL Fits Into a Broader Quantum Security Strategy
Harvest-now, decrypt-later is one part of the broader quantum security challenge.
Quantum security includes identifying vulnerable cryptography, preparing for post-quantum standards, reducing exposure to Q-Day, securing long-lived data, and building crypto-agility across the enterprise.
HNDL should be treated as the urgency driver. It explains why quantum readiness matters before quantum computers are fully mature.
Organizations that begin preparing now can reduce the amount of valuable data exposed to future decryption. Organizations that wait may discover that the most sensitive data was already collected years earlier.

Get your quantum readiness assessment
The assessment includes:
- Overview of your cryptographic landscape
- Quantum-safe deployment recommendations
- Guidance for securing legacy apps & infrastructure
HNDL FAQs
Harvest now, decrypt later is a cyberattack strategy in which adversaries steal or intercept encrypted data today and store it until future quantum computers can decrypt it. It creates immediate risk for data that must remain confidential for years or decades.
Yes. Harvest now, decrypt later and store now, decrypt later describe the same basic threat model. Both refer to collecting encrypted data now and decrypting it later when quantum computing capabilities mature.
HNDL is a threat because the data can be stolen now even if it cannot be decrypted yet. If that data remains valuable in the future, quantum decryption could expose information years after the original theft.
Data with a long confidentiality lifespan is most at risk. This includes government records, financial information, healthcare data, genetic data, defense research, intellectual property, legal records, and long-term identity data.
Q-Day is the point when quantum computers become powerful enough to break widely used public-key cryptography. HNDL is the threat that attackers can collect encrypted data before Q-Day and decrypt it after Q-Day.
Organizations can defend against HNDL by inventorying cryptographic assets, prioritizing long-lived sensitive data, reducing unnecessary retention, testing post-quantum cryptography, adopting crypto-agility, and engaging vendors on PQC migration plans.
Post-quantum cryptography helps reduce future HNDL risk by replacing quantum-vulnerable algorithms with quantum-resistant ones. However, it cannot protect data that has already been stolen unless that data was protected with quantum-resistant or sufficiently resilient methods before collection.
The first step is cryptographic discovery. Organizations need to identify where encryption is used, which algorithms protect sensitive data, and which systems contain long-lived information that should be prioritized for migration.


